The Gateway page allows you to configure Forward Nodes in Karnak. A Forward Node represents a DICOM Application Entity (AE) that receives DICOM instances and routes them to one or more destinations. See How Karnak works for the deployment workflow and the pipeline each instance goes through.
Forward Node
This page lists all the forward nodes configured in Karnak and allows you to create, edit, and delete them.
1. Create a Forward Node
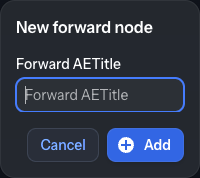
Click the New forward node button. A popup will appear:
Enter a unique value in the Forward AETitle field. AE Titles must not exceed 16 characters and cannot contain control characters or a backslash.
Click the Add button
The new forward node appears in the list and is automatically selected. Optionally, add a description and save your changes.
Info
The Forward AETitle must be unique across all forward nodes in the Karnak instance.
2. Create a group
When the list grows, you can organize forward nodes into groups (a single level of
folders) to keep related nodes together:
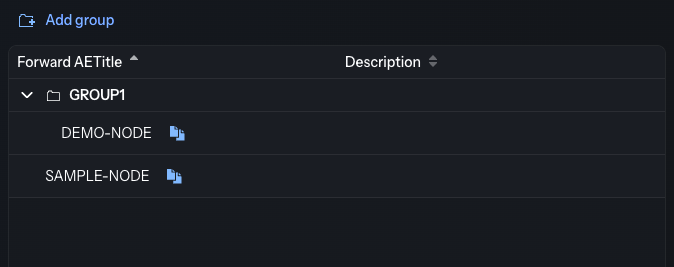
Click Add group to create a new group and give it a name.
Drag a forward node onto a group to assign it to that group.
Right-click a group to Rename group or Delete group; deleting a group only
removes the folder — the nodes it contained move back out, they are not deleted.
Right-click a node and choose Remove from group to take it out of its group.
Groups are purely organizational; they do not change how forward nodes behave. The same
grouping is available for Projects and Profiles.
3. Forward Node List
All configured forward nodes and groups are displayed in the left panel.
Select a forward node from the list to view and manage its configuration in the right panel.
Info
The copy icon
next to each forward node allows you to quickly copy its DICOM configuration (AE Title, host and the listener port — DICOM_LISTENER_PORT, 11119 by default, see the installation page) to the clipboard for use in DICOM clients. Adapt the host if the sending node reaches Karnak through another address.
4. Forward Node Parameters
In the details view, you can modify:
Forward AETitle: The Application Entity Title of the forward node
Description: An optional description to help identify the node’s purpose
Click the Save button to apply your changes.
5. Sources and Destinations
Each forward node can be configured with:
Sources: Control which DICOM nodes are authorized to send data to this forward node
Destinations: Define where received DICOM instances should be forwarded
5.1 Navigation
Use the tabs to switch between the Destinations and Sources views for the selected forward node.
5.2 Filtering
Destinations tab: a free-text filter matching a destination’s description, AE Title, hostname, port, URL, headers and notification settings.
Sources tab: a free-text filter matching a source’s description, AE Title and hostname.
5.3 List
All destinations or sources associated with the forward node are displayed here.
Click any item in the list (or a New button) to open its configuration form. The form
replaces the list panel in place; click Cancel to return to the list.
5.4 Actions
The available action buttons depend on the active tab.
Destinations tab:
Create a new destination using either the DICOM or DICOM WEB (STOW) protocol. See the Destinations page for detailed configuration instructions. The portable distribution shows an additional LOCAL button that creates a destination storing the instances in its local DICOM folder.
Sources tab:
Create a new source to control which DICOM nodes can send data to this forward node. See the Sources page for detailed configuration instructions.
6. Forward Node Actions
Three action buttons are available:
Action
Description
Save
Saves changes made to the forward node parameters
Delete
Deletes the selected forward node and all associated configurations
Cancel
Reverts unsaved changes to the forward node parameters
Info
While a transfer is running through the forward node, Save and Delete are disabled and read Transfer in progress; they become available again once the transfer is complete.
Warning
Deleting a forward node will also remove all associated sources and destinations, as well as the related entries in the Monitoring view. This action cannot be undone.
Subsections of Gateway
DICOM and DICOMweb Destinations
This page allows you to configure destinations for your forward nodes. Destinations define where DICOM instances are sent and how they are processed during transfer.
Info
To access this page, first select a forward node from the Gateway page, then open the Destinations tab (it is selected by default).
Depending on the protocol used, two types of destinations can be created:
A DICOM Destination uses the traditional DICOM protocol to forward instances to another DICOM node.
Creating a DICOM Destination
AETitle, Hostname and Port are mandatory when creating a DICOM Destination.
Configuration Options
1. Destination Parameters
These fields define where Karnak should send the DICOM instances.
AETitle: The Application Entity Title that identifies the destination DICOM node (16 characters max, no whitespace).
Description: An optional label shown in the destination list.
Hostname: The IP address or hostname of the destination server.
Port: The network port used by the destination DICOM service (must be between 1 and 65535).
Concurrent connections: The number of parallel DICOM associations Karnak opens to this destination (between 1 and 50; 1 means a single connection). Increasing this value improves throughput when forwarding large studies, but must stay within the destination PACS’s concurrent-association limit.
Condition (labeled Condition (Leave blank if no condition)): An optional field that can contain an expression. If the condition is met, the destination will be activated. See Conditions for more details.
2. Transfer Syntax
This field defines the transfer syntax used when sending DICOM instances to this destination. The transfer syntax determines the encoding and compression format of the DICOM data.
It is recommended to choose “Keep original transfer syntax” unless you have specific requirements for compression or compatibility with the destination system.
When selecting a specific transfer syntax, ensure that the destination system supports it to avoid decompression or compatibility issues. When you select a compressed transfer syntax, the Transcode only uncompressed checkbox becomes available and is checked automatically so that instances that are already compressed are not re-encoded; uncheck it only if every instance must be transcoded. The checkbox is disabled for Keep original transfer syntax and Explicit VR - Little Endian.
Info
Transcoding may increase processing time and resource usage, especially for large datasets. Use it judiciously based on your workflow needs.
3. Use AETitle Destination
When this option is checked, use the destination AETitle as the calling AETitle instead of the Forward Node AETitle during the DICOM association.
4. Notifications
Check Activate notification to receive automatic email summaries of forwarded
instances, including success and error reports.
Configuration fields (on screen each label is prefixed with Notif.: and shows its
default inline, e.g. Notif.: error subject prefix (Default: **ERROR**)):
Field
Description
Default Value
List of emails
Comma-separated list of recipient email addresses (required when notifications are active)
None
Error subject prefix
Prefix added to email subjects when an error occurs
**ERROR**
Rejection subject prefix
Prefix added when an instance is rejected due to filters or criteria
DICOM attributes to inject into the subject pattern (PatientID, StudyDescription, StudyDate, StudyInstanceUID)
PatientID,StudyDescription
Interval
Time in seconds to wait before sending notification (aggregates multiple instances)
45
Info
The interval setting helps reduce email volume by aggregating notifications. All instances received within the specified interval are summarized in a single email.
Info
Each email reports only what is new since the previous notification for a given
series (the delta), so outcomes that were already reported are not counted again when
the series is touched by a later transfer. A series touched only by retries or duplicate
re-sends has nothing new to report and therefore does not trigger a notification.
5. Virtual Destination
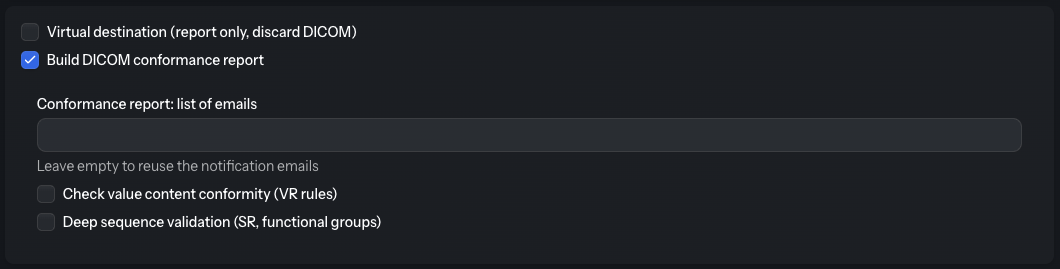
When Virtual destination (report only, discard DICOM) is checked, the destination
does not forward anything to a real node. Each study is still received and validated,
but the only output is the DICOM conformance report, which
is emailed. Delivery settings (transfer syntax, notifications, etc.) do not apply, and the
conformance report is mandatory and cannot be turned off while the destination is virtual.
This is useful to validate DICOM conformance — for testing, validation-only deployments,
or audit purposes — without sending any data.
Info
On screen, the Virtual destination and Build DICOM conformance report options
share a single box, displayed right after Notifications and before Tag Morphing
and De-identification.
6. DICOM Conformance Report
Enable Build DICOM conformance report to validate every study sent to this
destination against the DICOM standard and email an HTML report. When enabled, options
appear to set the report’s recipient emails, to also check value content conformity
(VR rules), to perform deep sequence validation, and to check for identifying data
burned into the image (this last option runs OCR through the external de-identification
image service, which must be reachable at OCR_URL, http://localhost:8000 by default).
See the dedicated Conformance Report page for what each option
does, when the report is sent, and what it contains.
7. Tag Morphing
Tag morphing allows you to modify specific DICOM tag values defined in a profile. With this mode, it is not mandatory to de-identify patient information like in De-identification mode.
The applied profile and its version are displayed below the selection
If no project exists yet, the same no-project popup shown for
de-identification appears, letting you create one or cancel.
Info
Activate tag morphing and Activate de-identification are mutually exclusive options. Only one can be active at a time.
8. De-identification
De-identification removes or replaces patient-identifying information in DICOM instances according to configurable rules and profiles. It is not possible to preserve the patient identity in the profile when this option is activated.
Info
Activate de-identification and Activate tag morphing are mutually exclusive options. Only one can be active at a time.
A popup will appear with two options, either create a project or continue without activating de-identification.
If a project exists:
Configure de-identification as shown below:
Project Selection
Select the project that defines the de-identification profile to apply. The profile name and version are displayed below the selection.
Each project is associated with:
A de-identification profile
A secret key used for pseudonymization and UID generation
See the Projects page for more information about project configuration.
Pseudonym Type
Pseudonyms replace patient identifiers while maintaining the ability to link de-identified data back to the original patient (when necessary and authorized).
Choose how Karnak should retrieve or generate pseudonyms:
This field (labeled Issuer of Patient ID by default) provides a default value for the Issuer of Patient ID when it’s not present in the DICOM instance. It is only shown when the pseudonym type is Pseudonym is already stored in KARNAK.
Usage:
This value is used when retrieving the pseudonym using the External Pseudonym cache. The pseudonym is queried based on:
Patient ID (from DICOM tag 0010,0020)
Issuer of Patient ID (from DICOM tag 0010,0021 or this default value)
The combination of Patient ID and Issuer ensures unique patient identification across different healthcare systems.
Ignore the Issuer of Patient ID (cache lookup)
This option is only available when the pseudonym type is Pseudonym is already stored
in KARNAK. On screen it is the Ignore Issuer of Patient ID checkbox. When checked,
the Issuer of Patient ID of the incoming image is ignored when building the key used
to look up the pseudonym in the cache.
It is enabled by default, so the same Patient ID is matched even when it is registered
under a different (or missing) issuer in the External Pseudonym cache
than in the images you receive. Uncheck it if you need the issuer to be part of the lookup
key. When this option is checked, the Issuer of Patient ID by default field is cleared
and disabled, since it no longer takes part in the lookup.
9. Authorized SOPs
Filter which DICOM instance types (SOP Classes) are forwarded to this destination.
Configuration:
Enabled: Only instances matching the specified SOP Classes are transferred. At least one SOP Class must be selected, otherwise the destination cannot be saved.
Disabled: All SOP Classes are transferred without restriction
10. Enable the Destination
The Enable destination checkbox allows you to temporarily disable a destination without deleting it. The state is also visible in the destination list with a green (enabled) or red (disabled) indicator.
Use this feature to:
Temporarily pause forwarding during maintenance
Test configurations without affecting production destinations
Keep backup destination configurations ready but inactive
11. Action Buttons
Three actions are available to manage the destination:
Button
Description
Save
Saves all changes made to the destination configuration
Delete
Permanently deletes the selected destination
Cancel
Reverts all unsaved changes to the last saved state
Info
While a transfer is running through the forward node, Save and Delete are disabled and read Transfer in progress; the Activity column of the destination list shows a spinner during that time.
Warning
Deleting a destination cannot be undone. All configuration settings will be permanently removed.
STOW Destination
A STOW Destination forwards instances over DICOMweb (STOW-RS) to a web server such as a DICOMweb-enabled PACS or a Kheops instance.
Creating a STOW Destination
The URL is required for STOW Destination creation. Most configuration options are identical to DICOM Destinations. Only the differences are detailed below.
Configuration Differences
1. Destination Parameters
URL: The DICOMweb STOW-RS endpoint where DICOM instances will be sent (e.g., https://pacs.example.com/dicomweb/studies).
Condition: An optional expression that activates the destination when met. See Conditions for more details.
Use HTTP/2
When Use HTTP/2 is checked, STOW-RS uploads use HTTP/2 instead of HTTP/1.1.
Warning
Leave this unchecked (HTTP/1.1) when the archive sits behind a reverse proxy that
caps the number of HTTP/2 requests per connection (e.g. KHEOPS / nginx
http2_max_requests=1000), which can silently drop instances beyond the limit.
HTTP Headers
The Headers field contains HTTP headers added to each STOW-RS request.
Format: Headers are defined using XML-style key-value tags as shown below:
Click the Generate Authorization Header button to automatically generate properly formatted authentication headers.
Warning
If a header with <key>Authorization</key> already exists, an error will be displayed. The generator will append to existing headers if they don’t conflict.
Supported Authorization Types: the dialog has an Authorization Type selector
(Basic Auth or OAuth 2) and a Generate Headers button that appends the
generated header.
If the destination is a Kheops endpoint, it is possible to configure multiple albums by selecting the option “Switching in different KHEOPS albums”.
Explanations for configuring Kheops-related parameters can be found in the Kheops section.
Restrict Which DICOM Sources May Send
The Sources tab displays all configured sources for the selected forward node.
A source is used to control which entities can send DICOM data to the forward node. It validates that received DICOM instances come from a known Application Entity Title (AET).
Info
If no sources are defined, the forward node will accept DICOM instances from any AET without restrictions.
Create a source
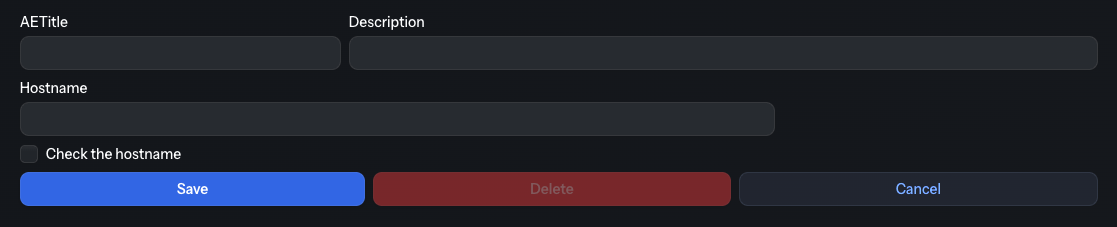
To create a new source, click the Source button and configure the following fields:
Field
Description
Required
AETitle
Application Entity Title of the source DICOM node (16 characters max)
Yes
Description
Optional description to identify the source
No
Hostname
Hostname or IP address of the source DICOM node
No*
*Fill in the Hostname when you enable the “Check the hostname” option. When enabled, Karnak validates both the AET and the hostname (or IP address) of the calling node during the DICOM association, and refuses the connection when the hostname does not match.
Source validation behavior
When a DICOM instance is received by the forward node:
With sources configured: Only instances from registered AETs (and hostnames, if enabled) are accepted. Instances from any other node are refused with the DICOM status Not Authorized (0124H) and are listed in the Monitoring view as not transferred, with the reason Source not authorized: .
Without sources configured: All instances are accepted.
This provides flexible security control for your DICOM workflow.